Risk & Compliance Management
Meeting cross-industry regulatory mandates (SOX, SOC 2, GDPR, HIPAA, ISO 27001) demands a unified, audit-ready identity governance architecture. IDHub enforces continuous compliance across hybrid infrastructure, neutralizing toxic access combinations and automating Segregation of Duties (SoD). Move beyond manual spreadsheet audits and access certification fatigue to a state of provable, automated identity security.

The Compliance Reality: Eradicating Entitlement Sprawl
Legacy identity frameworks fracture under the weight of modern regulatory scrutiny. Organizations face critical vulnerabilities at the intersection of access creep, orphaned accounts, and manual oversight.
Achieving true identity security requires a proactive approach. By centralizing governance and utilizing exact mechanisms to automate risk mitigation, organizations can eliminate access certification fatigue, enforce continuous policy structures, and maintain an impeccable, real-time audit posture across all cloud and on-premise environments.
Continuous Compliance Through Automated Governance
Manual auditing drains security teams and leads to dangerous rubber-stamping. IDHub eliminates these risks by delivering compliance automation purpose-built to elevate your overall IAM maturity stage. IDHub Functions for Risk Mitigation are as follows:
Automated Segregation of Duties (SoD)
Review Access requests to revoke entitlements or accounts which is no longer required.
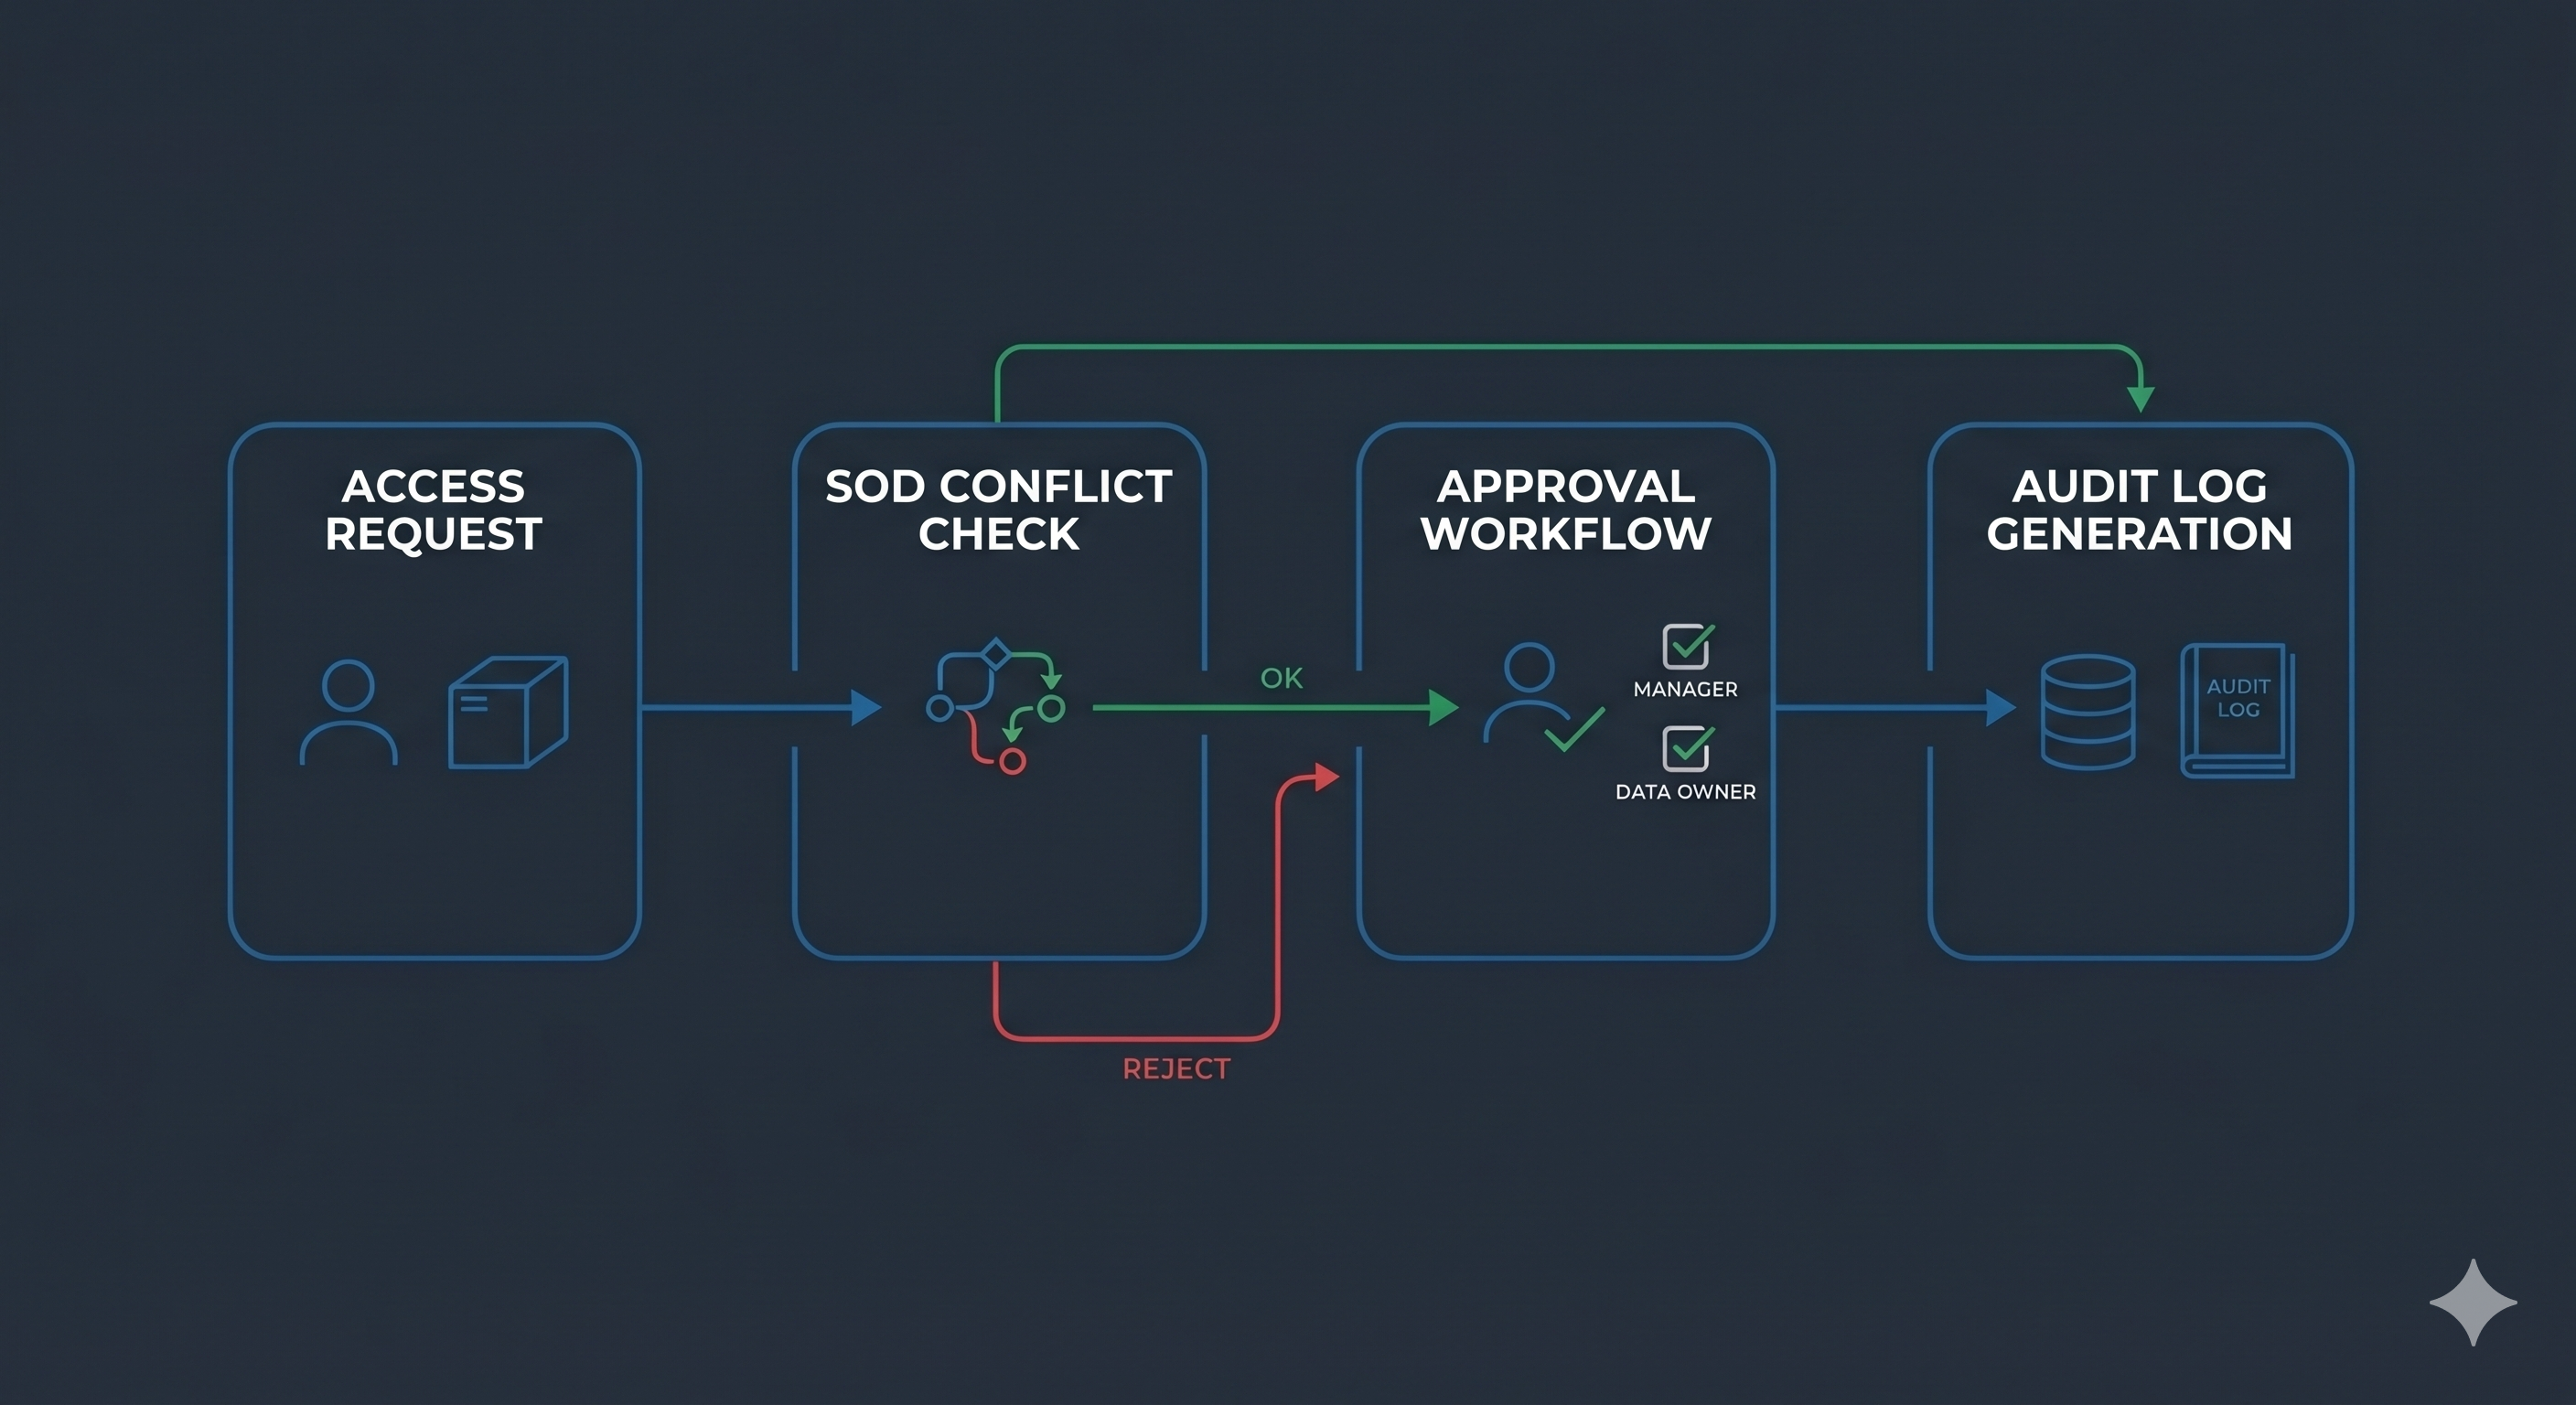
Map complex business logic into automated workflow condition nodes that instantly flag and halt SoD violations based on real-time identity attributes.
Review access across different target system environments to detect out-of-band entitlement shifts or any lurking expired accounts.
Certifications
Deploy continuous access reviews triggered automatically by lifecycle events (e.g., department transfers, promotions).
Eliminate certification fatigue and "rubber-stamping" by requiring reviewers to validate only critical changes and critical, high-privilege access.
Instantly trigger de-provisioning workflow the exact moment an entitlement or account is revoked during a certification cycle.
RBAC/ABAC Convergence
Synthesize Role-Based Access Control (RBAC) baselines with Attribute-Based Access Control (ABAC) conditionals to evaluate access requests against real-time variables.
Automate day-one birthright provisioning while applying granular, policy-driven restrictions for elevated or temporary privileges.
Ensure access requests are in strict accordance with shifting business attributes, effectively neutralizing manual permission bloat.
Cross-Industry Audit Readiness
Align automated workflows to satisfy compliances, including SOX, SOC 2 Type II, HIPAA, GDPR, and ISO 27001.
Centralize decentralized identity data from both legacy on-premise and modern cloud environments into a unified, tamper-proof audit trail.
Translate raw, technical entitlement data into highly readable compliance reports that definitively prove access boundaries to external auditors on demand.
Orphan Account Remediation
Leveraging application reconciliation, detect unmanaged, dormant, or unauthorized accounts across the entire hybrid IT infrastructure.
Revoke any accounts or entitlements which might be there because of offboarding, contractor terminations, or undocumented out-of-band IT modifications.
Review workflows to lock down any orphan identities before they can be exploited by threat actors.
Hybrid Infrastructure Architecture & Deployment Sovereignty
Regulatory constraints do not stop at the edge of the cloud. Disconnected legacy systems create compliance black holes.
IDHub provides a unified identity fabric bridging complex hybrid environments. By utilizing a vast library of universal connectors, IDHub seamlessly integrates on-premise infrastructure with modern SaaS applications, ensuring that access policies and compliance rules are orchestrated uniformly across the entire technological landscape.
Furthermore, IDHub supports flexible deployment architectures to accommodate strict data control mandates. Whether operating via IDHub Cloud (SaaS) for rapid scalability or deployed On-Premise/Air-Gapped to satisfy absolute data sovereignty and localization requirements, the platform ensures total command over your identity telemetry.
Neutralize Insider Threats and Audit Vulnerabilities
Delayed deprovisioning and excessive, accumulated permissions leave organizations highly vulnerable to data breaches and catastrophic audit failures. Manual compliance tracking not only slows down operations but exponentially increases the risk of toxic access combinations. IDHub helps enterprises surgically close these gaps by strictly enforcing continuous compliance policies:
- Eliminate certification fatigue with automated, event-driven access reviews.
- Preemptively block toxic access combinations with hard workflow condition nodes.
- Deliver auditor-ready reports detailing every policy assignment and validation.
- Orchestrate compliance rules uniformly across cloud and on-premise targets.
Neutralize Insider Threats
Compliance Mechanisms for the Modern Enterprise
Enforce Policy-Driven Access Controls
IDHub anchors user access directly to authorized roles, attributes, and policies. This dynamic convergence ensures access is granted and revoked in strict alignment with organizational governance rules, preventing over-permissioning from day one.
Prevent Conflicting Access
Establish hard boundaries within the identity architecture. IDHub’s SoD engine actively scans and blocks conflicting permissions before they are provisioned, preventing users from gaining capabilities that violate compliance frameworks (e.g., initiating and approving the same financial transaction).
Automate Access Reconciliation
Timely access reviews are critical to preventing compliance drift. IDHub executes continuous access reconciliation to identify data mismatches, flag risky access accumulations, and automatically trigger remediation workflows to restore a compliant state.
Centralized Audit Telemetry
Consolidate compliance data into a single pane of glass. IDHub monitors transactional and audit data across connected hybrid systems, providing general visibility and exportable logs that give auditors immediate proof of exactly who accessed what, when, and who approved it.
Cybersecurity Tools